Home
» Today
»
Cyber Attack on French Supermarkets: What We Know About the Disruption
Cyber Attack on French Supermarkets: What We Know About the Disruption
As of October 13, 2026, the confirmed consumer impact of the French supermarket cyberattack is disruption to refrigeration and the loss of perishable stock at affected stores. Reports published October 12 described connected chillers being remotely forced into defrost mode, with some temperatures reported as high as 50°C (122°F). Intermarché and Coopérative U confirmed affected stores; Leclerc also said a cyberattack affecting a refrigeration-equipment supplier had repercussions in some stores. The Paris prosecutor’s office opened an investigation, and France’s cybersecurity agency, ANSSI, was asked to examine the incident. The number of affected locations, the full technical cause, and the attackers’ identity remain unsettled.
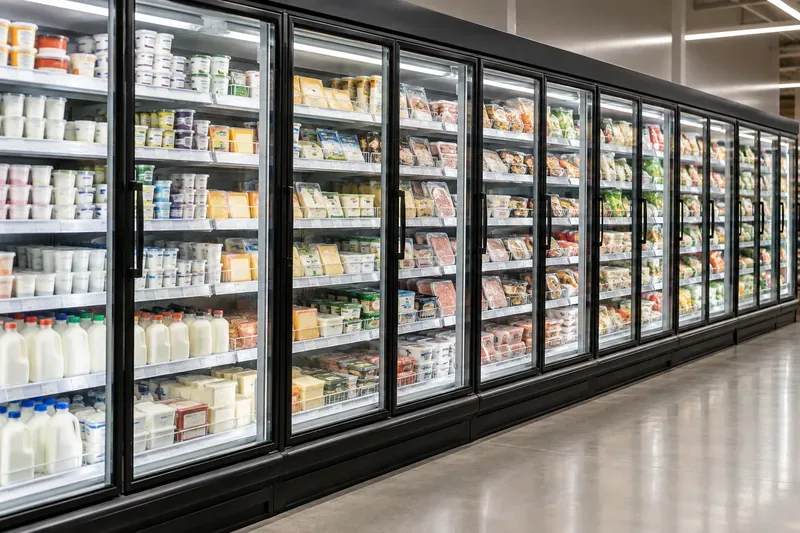
Refrigerated display cases in a supermarket; this neutral scene illustrates the equipment at the center of the reported disruption.
What happened
Overnight from Sunday into Monday, October 11–12, attackers interfered with remote controls used for commercial refrigeration systems in French supermarkets. Retailers and news reports said units were put into forced defrost, causing temperatures to rise and food to spoil. Reuters reported temperatures reaching 50°C in some units and cited the Paris prosecutor’s description of a large-scale attack affecting connected refrigerators at several major food retailers. The prosecutor also reported food losses and fires at some locations.
Intermarché said affected branches had to discard fresh and frozen products. Coopérative U’s leadership also confirmed refrigeration disruptions in several stores. Leclerc said a cyberattack had affected one of its refrigeration equipment suppliers, with consequences for systems at several stores. These statements show the issue was more than a normal refrigeration fault: remote digital controls were implicated. They do not, by themselves, establish that the retailers’ checkout, payment, loyalty, or customer account systems were compromised.
What is known—and what is not
Question
What reporting supports as of October 13
What remains unclear
What was disrupted?
Connected refrigeration and defrost controls at stores operated by several French retailers.
The complete list of affected locations, models, and system configurations.
What was the practical impact?
Food losses were reported; affected shops discarded perishable and frozen stock. Fires were also reported at some sites.
The final amount of food lost, financial cost, and duration of every store’s disruption.
Who was responsible?
Authorities were investigating a cyberattack.
No verified public attribution to a person, group, or state.
Was customer data stolen?
Available incident reporting focused on refrigeration operations.
No public evidence in the cited reports established theft of shopper data or compromise of payment systems.
Was a supplier involved?
Reports linked affected refrigeration management systems to equipment or software supplied by Danish company Danfoss; Danfoss said incidents involved systems running outdated firmware.
The precise entry point and whether a software vulnerability, exposed remote access, configuration issue, or another factor enabled this specific attack.
Store counts differ between early reports and may change as companies inspect equipment. Reuters reported Intermarché saying refrigeration units at 150 stores were affected for about six hours; other accounts gave broader counts that combined Intermarché and Netto locations. Treat any total as provisional until retailers or investigators publish a final tally.
Why refrigeration systems can become a cyber risk
Modern refrigeration equipment often includes sensors and digital controllers that track temperature and allow authorized technicians to monitor or adjust settings remotely. Remote access can help stores manage equipment across many locations, but it also connects physical operations to software, networks, credentials, and maintenance processes. If a remote-management account or connected system is misused, a digital action can produce a physical consequence: food warms, equipment cycles unexpectedly, or staff must close a case and inspect stock.
This is an operational technology issue. Operational technology (OT) means digital systems that monitor or control equipment in the physical world. The incident demonstrates why organizations need to treat building and refrigeration controls as part of their cybersecurity program. It does not establish that all connected refrigeration systems are unsafe, nor that ordinary shoppers’ home refrigerators or devices are exposed to the same issue.
What shoppers should do now
Check the specific store before traveling. Use the retailer’s official store page, app, or customer-service channel for local opening, product, or service updates. The reports do not establish a nationwide closure or a disruption to all grocery operations.
Follow product notices. If a retailer announces a recall or withdrawal, follow the instructions for the named product, lot, and dates. Do not assume every refrigerated product sold in France is affected.
Use normal food-safety caution. If you bought a product from a clearly malfunctioning display or received a direct notice that it was affected, do not taste it to decide whether it is safe. Keep packaging and proof of purchase, and contact the retailer or the relevant food-safety service for guidance.
Do not spread unverified claims. A refrigerator incident does not prove that card data, loyalty accounts, or personal information were stolen. Look for a direct notice from the retailer before changing passwords or taking other account-specific steps.
France’s consumer-protection agency, DGCCRF, explains why preserving the cold chain matters and provides consumer guidance in its page on maintaining the cold chain. That general advice is useful context; it is not a statement that a particular product or store was affected in this incident.
What retailers and suppliers need to establish
Investigators and operators will need to reconstruct how remote access was obtained, identify which systems and firmware versions were exposed, and determine whether unauthorized commands reached refrigeration controllers directly or through a management layer. They will also need to confirm whether other stores or countries used the same vulnerable configuration. The public evidence available on October 13 did not yet settle these questions.
Danfoss told Reuters the incidents involved systems running outdated firmware and said security updates addressing the flaws had been issued. That is relevant to maintenance and exposure, but it is not a complete forensic account or proof that a particular flaw was the initial access route in every store. Retailers should apply vendor-recommended fixes through controlled procedures, review remote-access accounts, preserve logs, and verify physical temperatures after systems are restored. Disconnecting a controller may interrupt normal monitoring, so businesses should coordinate with qualified refrigeration technicians and incident responders rather than improvise changes on live equipment.
ANSSI has previously encouraged food-sector organizations to prepare for cyber incidents and continuity problems. Its June 2026 crisis-exercise kit for the agri-food sector is general preparedness guidance, not an incident report about these supermarkets. It highlights the value of rehearsed decision-making, communication, and continuity plans when technology disruption affects food operations.
What has not been verified
As of October 13, the cited reporting did not identify the attackers or establish a motive. It did not confirm that this was ransomware, a data breach, or a politically directed operation. Reports of cybersecurity problems at grocery businesses elsewhere in Europe should not automatically be treated as part of the same campaign; a connection requires evidence. Nor should reports naming an equipment vendor be read as proof that the vendor alone caused the attack: investigators must determine how systems were configured, maintained, and accessed.
What to watch for next
Statements from the Paris prosecutor’s office or ANSSI about the investigation and scope.
Retailer updates that identify affected stores, products, or customer actions.
A technical advisory from the equipment supplier describing affected product versions and verified remediation steps.
Confirmation about whether other countries or related systems were affected.
Evidence-based clarification on data exposure, payment services, or any wider disruption.
The practical takeaway for shoppers is straightforward: this was reported as an attack on supermarket refrigeration controls, with food losses at affected stores. Check local retailer notices and follow product-specific guidance. Until authorities or companies release more verified findings, the attacker, exact access path, final store count, and any broader customer-data impact should be treated as unknown.
Reporting status: information checked on October 13, 2026. This article reflects early public reporting; details may change as retailer reviews and the investigation continue.