Arena 5D is an event launched by Garena to thank players who have always wholeheartedly supported Arena of Glory Winter 2022. Through this article, you will have the opportunity to receive many valuable costumes and in-game items. Let's explore now.
Table of Contents
Event content of 5D Arena
Event Time
5D Arena will take place from September 30 to October 9, 2022.
How to join the event
- There are 5 D's in total that you need to collect, including: Class, Confrontation, Intelligence, Teamwork and Focus.
- Each letter D will require 5 pieces to unlock.
- For each opened D, you will receive 2 non-repeating spins.
- The final D - Focus will only be received on the day of the 2022 Winter Finals (October 9). You will need to watch the 2022 Winter Finals according to 5 time frames.
- The last letter D will help the player get double spins.
- You can trade with your friends when your D has more than 5 pieces.
Ways to collect pieces
You can collect pieces through the following ways:
- Follow fanpage and share event page to receive up to 8 random pieces.
- Participate in a quiz competition with other players to receive random pieces every day.
- Each correct/faster answer than your opponent will help you get any piece. You will have a maximum of 3 turns per day.
Event rotation mechanism
- Items received will not be duplicated.
- The fastest and luckiest player will spin the costume box and receive valuable costumes.
Event Rewards
- Through the spin, players can receive items such as:
- Name change card
- Gold x2 card
- piece of jade
- Grade A talisman drawing paper
- S-rank talisman drawing paper
- Custom champion chest
- Custom Costume Chest...
See also:
Instructions for participating in the 5D Arena event
To be able to participate in this event, players need to follow the steps below.
Step 1: Access the event link
https://9thang10.lienquan.garena.vn/
Step 2: Log in to your game account by clicking on the login section in the top right corner.
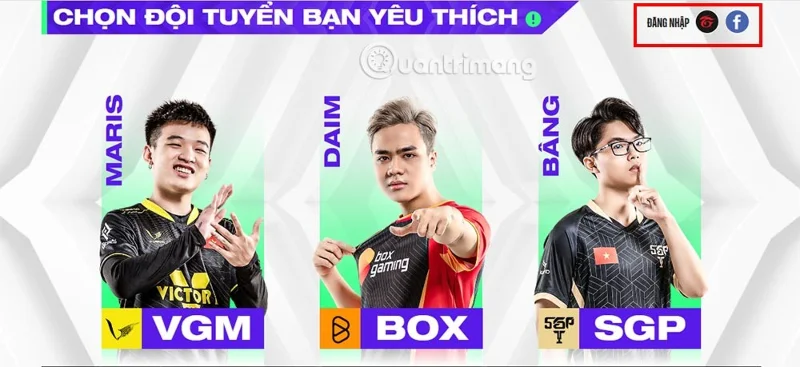
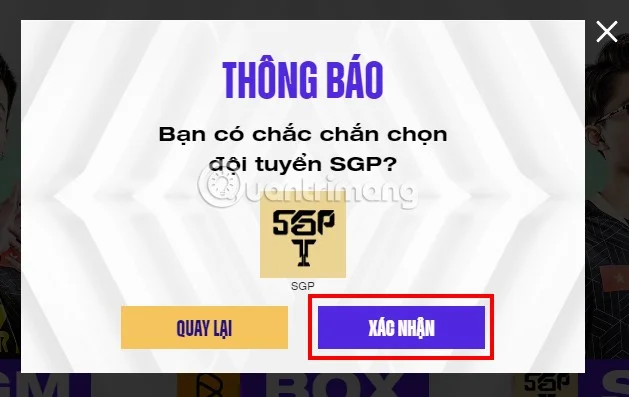
Step 3: Click on your favorite team to cheer for. You can choose between VGaming, BOX and Saigon Phantom.

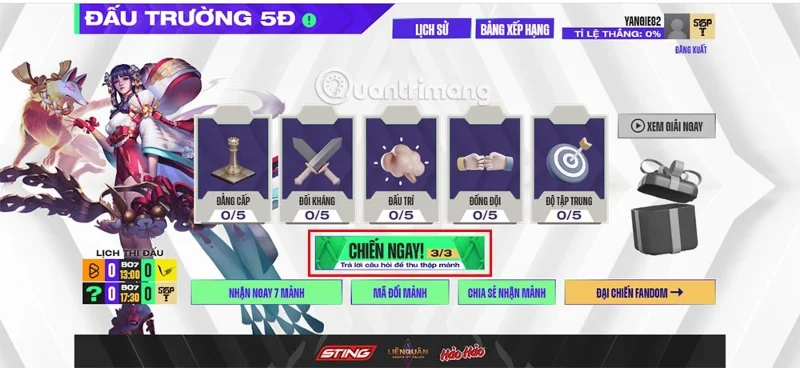
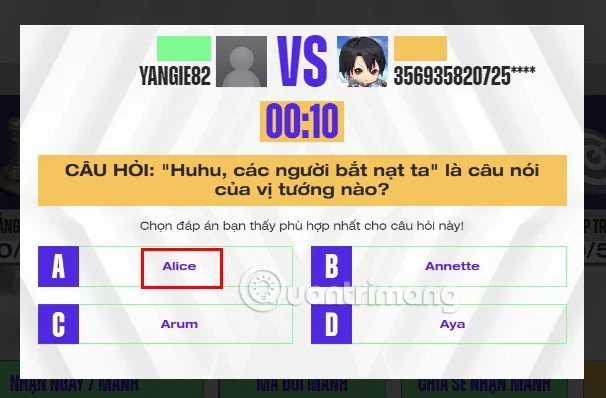
Step 4: You are redirected to the main interface of the event. Here, click on the Battle Now box to participate in answering questions with other players to receive random pieces.

The questions in the event will be related to the tournaments and the generals of Lien Quan. In case you are not familiar with the tournaments, you can refer to the answers to the event questions in the article below before participating in answering.

Note: Every day you will have 3 turns to collect pieces, so don't forget to visit the event link every day.
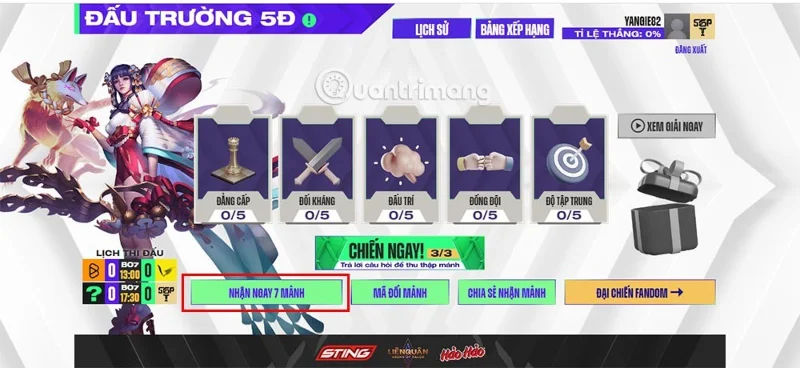
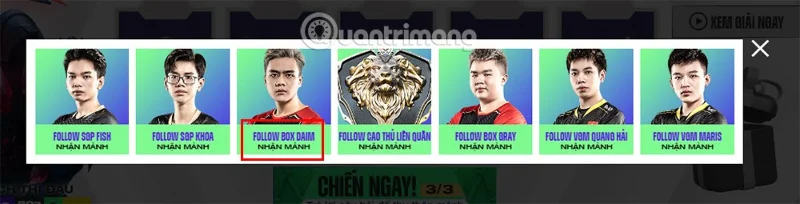
Step 5: You can also click on the Get 7-piece day section on the event interface.

Next, you just need to click Follow... to receive the pieces and follow the Fanpages of the players and receive random pieces for yourself.

Above is the complete guide on how to participate in the 5D Arena event that Quantrimang wants to send to you. Hope you will soon receive valuable items through this event.