Enable FIPS Mode on SLES 15 and Verify the Boot State
Follow SUSE’s SP7 procedure to enable FIPS mode, reboot safely, verify the active policy, and check whether your compliance requirement calls for validated modules.
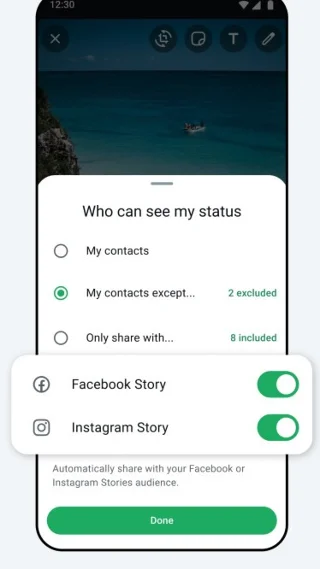
Meta has announced that users will soon be able to add their WhatsApp accounts to the Account Center, which is connected to their Facebook, Instagram accounts. With this integration, users will be able to cross-post WhatsApp statuses as Stories on Instagram and Facebook.
Accordingly, when you post a status on WhatsApp, there will be an option to share it on Instagram and Facebook if you want. This opens the door to sharing Instagram stories directly on WhatsApp, when Meta allows posting back from Instagram or Facebook.
The Account Center is where Facebook, Instagram, and Meta Quest are managed and aggregated. It appears on the settings page of the social media apps and allows you to easily log in to those apps. Meta has claimed that linking accounts will also simplify the login process for WhatsApp. You will be able to do this using the username and password of your other social media accounts.
Your account will not be linked by default as it needs to be done manually. Linking your account to the Account Center will not affect the end-to-end encryption of WhatsApp messages. So your data, chats and media will remain intact and not even Meta can access it.

Follow SUSE’s SP7 procedure to enable FIPS mode, reboot safely, verify the active policy, and check whether your compliance requirement calls for validated modules.
Compare YaST and cryptsetup for a new encrypted SLES data volume, choose LUKS1 or LUKS2, and verify unlock and mount behavior safely.
Create, refine, and verify a least-privilege AppArmor profile on SLES 15 SP7, with a clear note on SLES 16’s SELinux default.
Set up RMT on SLES 15, mirror entitled repositories, and verify HTTPS registration and package access from a test client.
Connect SLES 15 to AD with YaST’s SSSD-based logon management, then verify directory lookup, domain login, and Kerberos tickets.
Set up the right Live Patching path for SLES 16.0 or 15 SP7, apply eligible kernel fixes, and confirm what is active without confusing it with a reboot-required kernel update.
Load a custom SLES 15 kernel module without disabling Secure Boot. Match the running kernel, sign the .ko file, enroll a MOK key, and verify loading.
SLES 15 SP5 can migrate online to SP6, but each node must reboot. Use a tested rolling upgrade or blue-green cutover to keep workloads reachable.
Use SUSE’s supported STIG profile to scan SLES 15, test remediation, review remaining findings, and retain assessment evidence.
Trace a failed Cockpit connection through DNS, port 9090, the systemd socket, firewalld, TLS, and login settings using current SUSE guidance.








