Instructions for authenticating your Zalo account are extremely simple

Zalo is a social networking application used by many people today. Because of this, there are many hackers who want to steal their Zalo accounts to get their friends' information. Therefore, securing Zalo accounts is an extremely urgent task for users of this account.

To help protect everyone's Zalo account from being stolen or lost, Zalo has allowed users to set up security mode through account verification with ID card/CCCD card . Today, Download.vn will introduce an article with simple instructions on authenticating Zalo accounts , please refer to it.

Instructions for securing Zalo accounts from hackers

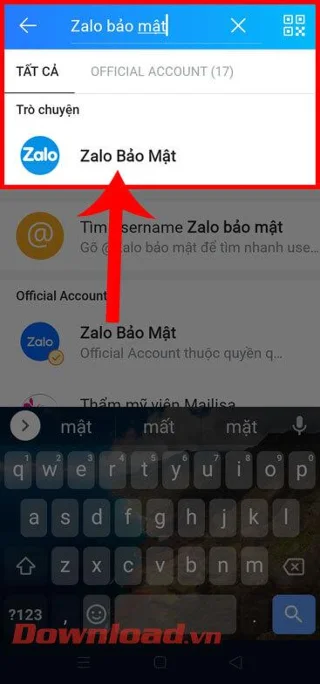
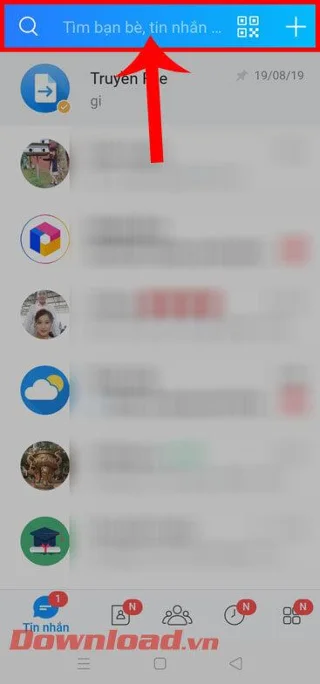
Step 1: First, open the Zalo application on your phone, then click on the search box on the screen.

Step 2: In the search box, enter the keyword " Zalo security ".
Instructions for authenticating your Zalo account are extremely simple Instructions for authenticating your Zalo account are extremely simple

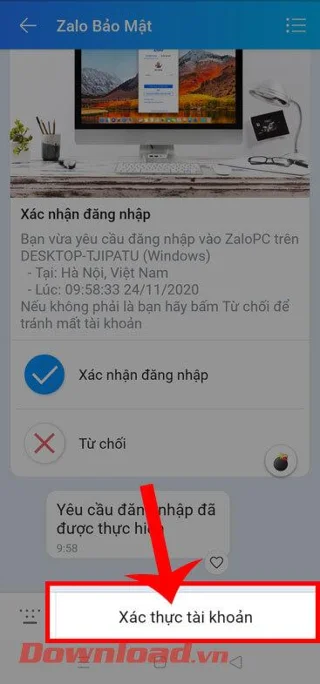
Step 3: In the secure Zalo conversation , tap the Account Verification button at the bottom of the screen.

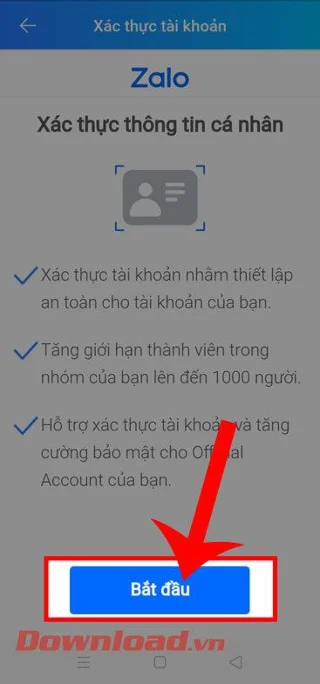
Step 4: To start the process of verifying your Zalo account, click the Start button .

Instructions for authenticating your Zalo account are extremely simple Instructions for authenticating your Zalo account are extremely simple

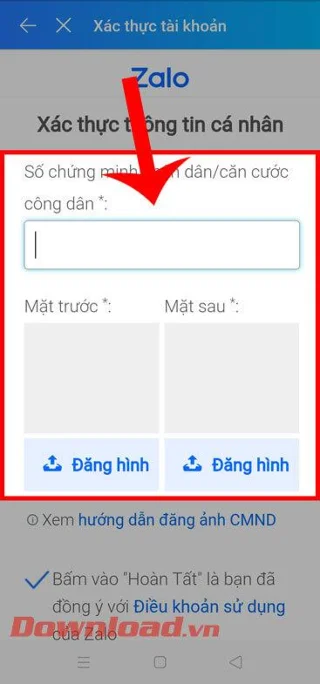
Step 5: In the screen of Verifying personal information , enter your ID card number or CCCD card . Then take a photo of the front and back of the ID card/CCCD .

Step 6: Then, drag the screen down, then click the Done button .

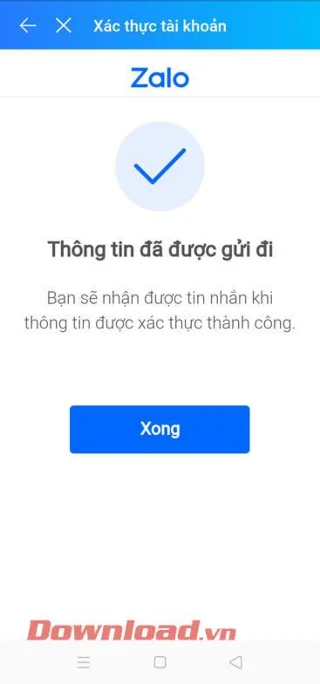
Step 7: Finally, when the account is successfully verified, the message " Information has been sent " will be displayed on the screen.

Instructions for authenticating your Zalo account are extremely simple Instructions for authenticating your Zalo account are extremely simple Instructions for authenticating your Zalo account are extremely simple

Wishing you success!

Leave a Comment

Enable FIPS Mode on SLES 15 and Verify the Boot State

Enable FIPS Mode on SLES 15 and Verify the Boot State

Follow SUSE’s SP7 procedure to enable FIPS mode, reboot safely, verify the active policy, and check whether your compliance requirement calls for validated modules.

Set Up a LUKS-Encrypted Data Volume on SLES

Set Up a LUKS-Encrypted Data Volume on SLES

Compare YaST and cryptsetup for a new encrypted SLES data volume, choose LUKS1 or LUKS2, and verify unlock and mount behavior safely.

Build a Custom AppArmor Profile on SUSE Linux

Build a Custom AppArmor Profile on SUSE Linux

Create, refine, and verify a least-privilege AppArmor profile on SLES 15 SP7, with a clear note on SLES 16’s SELinux default.

Build a Local SUSE Update Server with RMT on SLES 15

Build a Local SUSE Update Server with RMT on SLES 15

Set up RMT on SLES 15, mirror entitled repositories, and verify HTTPS registration and package access from a test client.

Join SLES 15 to Active Directory with SSSD in YaST

Join SLES 15 to Active Directory with SSSD in YaST

Connect SLES 15 to AD with YaST’s SSSD-based logon management, then verify directory lookup, domain login, and Kerberos tickets.

Enable SLES Live Patching and Verify a Kernel Fix

Enable SLES Live Patching and Verify a Kernel Fix

Set up the right Live Patching path for SLES 16.0 or 15 SP7, apply eligible kernel fixes, and confirm what is active without confusing it with a reboot-required kernel update.

Install and Sign Custom Kernel Modules on SLES 15 Secure Boot

Install and Sign Custom Kernel Modules on SLES 15 Secure Boot

Load a custom SLES 15 kernel module without disabling Secure Boot. Match the running kernel, sign the .ko file, enroll a MOK key, and verify loading.

Keep Services Available During a SLES 15 SP5 to SP6 Upgrade

Keep Services Available During a SLES 15 SP5 to SP6 Upgrade

SLES 15 SP5 can migrate online to SP6, but each node must reboot. Use a tested rolling upgrade or blue-green cutover to keep workloads reachable.

Apply the SLES 15 STIG Safely with OpenSCAP

Apply the SLES 15 STIG Safely with OpenSCAP

Use SUSE’s supported STIG profile to scan SLES 15, test remediation, review remaining findings, and retain assessment evidence.

Restore Cockpit Access to SUSE Linux Enterprise Server

Restore Cockpit Access to SUSE Linux Enterprise Server

Trace a failed Cockpit connection through DNS, port 9090, the systemd socket, firewalld, TLS, and login settings using current SUSE guidance.