Creator Likeness Protection: Practical Steps and UK Changes | 22 November 2026
Learn how creators can protect their face, voice and work from unauthorised AI replicas, document misuse and use platform tools and UK protections.
Verified and updated: November 22, 2026, 12:12 p.m. UTC (7:12 a.m. EST).
Bell Canada says an intruder accessed some of its systems on November 17 and stole data belonging to enterprise customers. Bell says it contained the incident, secured its systems and has seen no impact to customer services. The company has not disclosed how many organizations were affected or how much information was taken, so the full scope remains unknown.
Bell told BleepingComputer that a threat actor accessed multiple systems, including one used to order and provision telecommunications circuits, and removed some enterprise customer data. The report also describes a notice sent by Bell’s Information Security Team to a business customer. According to that notice, an unauthorized party accessed a pre-production environment of Bell’s Maximo system, which supports ordering and provisioning network connections. Bell has not publicly detailed the access method or the full timeline of its investigation. BleepingComputer’s report, including Bell’s statement.
The Bell notice described in the report says information potentially taken may include business names, job titles, corporate email addresses, phone numbers and business addresses. It may also include ticket titles, some IP addresses associated with network elements or systems, and limited related context. Bell said the affected dataset did not include account credentials, highly sensitive personal information, PDFs, file attachments or other supplementary material stored in Maximo.
Those details are tied to a reported notice and do not establish that every listed field was taken for every affected organization. Bell has not announced the number of impacted enterprise customers, the total amount of data stolen or a complete accounting of the records. Consumers should not assume their personal Bell account information was involved based on the information available so far.
Bell used the term “agentic” to describe the threat actor in its statement. The label alone does not establish which tools were used, whether artificial intelligence was involved, or how much autonomy any software had. Bell has not publicly named the actor, and it told BleepingComputer attribution was not known. Until more technical details are released, claims about a specific AI system or attack technique would be speculation.
Bell says it contained the incident and secured its systems after learning of the breach. The company is notifying affected customers and sharing indicators of compromise and threat-hunting information with enterprise customers and the Canadian Centre for Cyber Security, according to its statements reported by BleepingComputer. Bell has not publicly released those indicators, and the investigation is ongoing.
For affected organizations, the practical concern is targeted impersonation. Business contact details and information about telecom service requests can help make a fraudulent email or call sound credible. Bell’s customer notification reportedly urged organizations to be cautious about unsolicited requests and people impersonating the provider. Businesses that receive a notice should use established Bell contact channels to verify requests, alert staff who manage telecom accounts, and review their own monitoring for relevant indicators shared directly by Bell.
For individual subscribers, Bell has not reported a disruption to customer services or stated that general consumer account credentials were exposed in this incident. Be wary of unexpected messages claiming to be about a Bell breach; do not open attachments or share passwords or verification codes in response. If Bell contacts you about a specific impact, verify the message through a known official channel.
Bell says there was no impact to customer services from this incident.
Bell said the affected dataset did not contain credentials. The confirmed reporting concerns enterprise customer data; Bell has not said consumer account passwords were exposed.
Bell has not disclosed a total number of affected enterprise customers or the amount of data taken.
Learn how creators can protect their face, voice and work from unauthorised AI replicas, document misuse and use platform tools and UK protections.
AI reskinning puts synthetic characters into creators’ existing performances. Here’s how it works, why it matters and what UK creators can do.
UK ministers address AI creator impersonation as YouTube expands likeness detection. What changed in 2026, where rights fall short and what comes next.
Bell says a Nov. 17 cyber incident exposed some enterprise customer data, with no service impact reported. Learn how Bell customers can protect accounts and spot impersonation scams.
Bell Canada says a November 17 cyberattack exposed enterprise contacts, ticket details and some IP addresses. Here is what is known—and what remains unclear.
Bell says a Nov. 17 intrusion exposed some enterprise customer data, with no service disruption reported. Here is what is confirmed and what remains unknown.
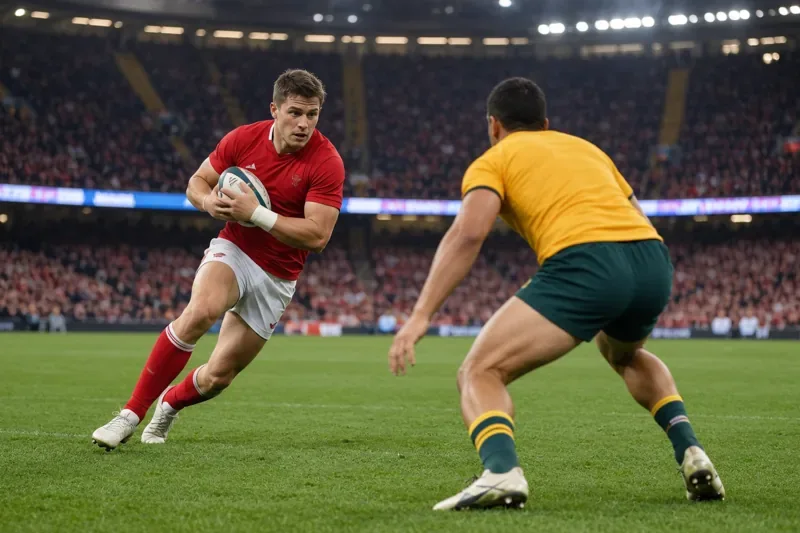
Australia edged Wales 29–26 in Cardiff, withstanding a late comeback after four tries from each side. See the score, key moments, and what comes next.
Why Australia beat Wales 29–26 in the 2026 Nations Championship: the tactical turning points, match statistics, late penalty, and what comes next.
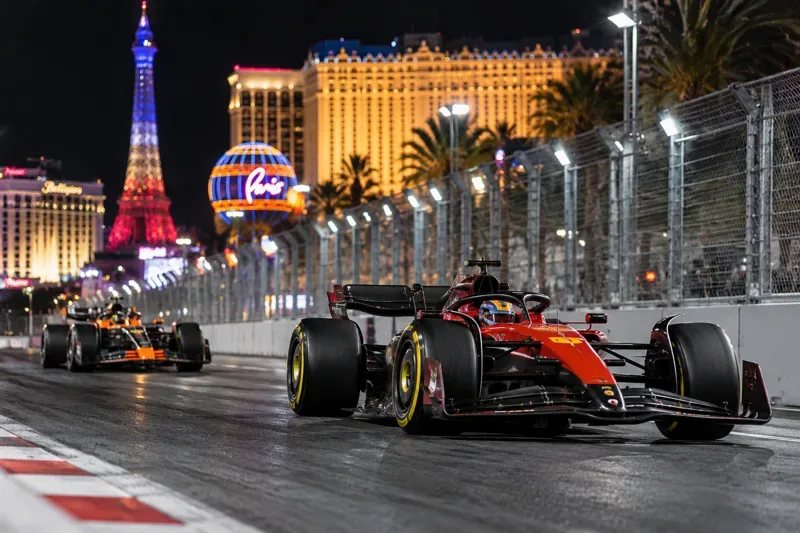
After Verstappen’s Las Vegas win, see the verified 2026 F1 drivers’ and constructors’ standings, title status, and the nine-point Red Bull–McLaren battle.
Max Verstappen won the 2026 Las Vegas Grand Prix by 0.639 seconds. See the FIA final classification, points, penalties, fastest lap and race highlights.