Enable FIPS Mode on SLES 15 and Verify the Boot State
Follow SUSE’s SP7 procedure to enable FIPS mode, reboot safely, verify the active policy, and check whether your compliance requirement calls for validated modules.
Signing in to Facebook from Gmail is a very handy feature, especially for those who use Gmail on a daily basis. However, this is also a hidden feature and is not available in this email service, to be able to access Facebook from Gmail, we need to set up some changes as instructed below.
Download Facebook for iOS
Download Facebook for Android
Download Facebook for Windows Phone
Step 1: Log in to your Gmail account on the web browser.
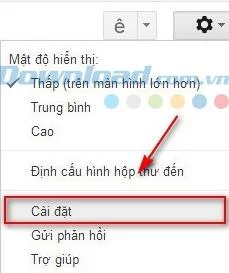
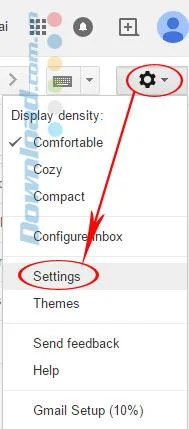
Step 2: C lick the left mouse on the icon Settings (Settings).
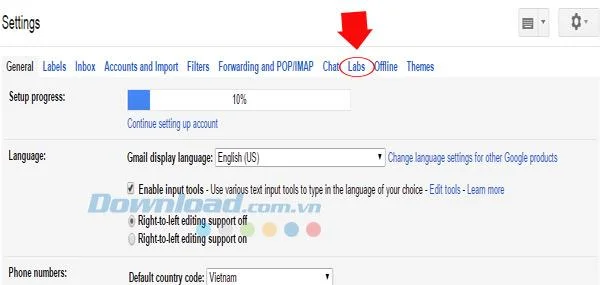
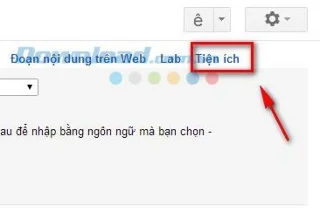
Step 3: A new window appears, click the Labs tab to continue the installation.
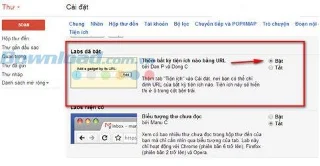
Step 4: Find the item Add any gadget by URL ( Add any gadget by URL ) and select On ( Enable ).
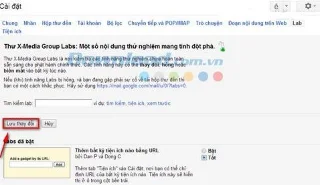
Step 5: At this time, a notification box will appear, select Save changes.
Step 6 : After saving changes , the system will automatically reload and return to the homepage of Gmail . So need to cl ick on the settings icon (shaped pinion) right interface of Gmail again.

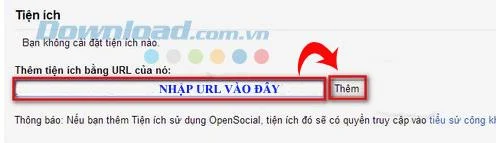
Step 7: Enter the following URL in the Add gadget box with its URL , then click Add.
http://hosting.gmodules.com/ig/gadgets/file/104971404861070329537/facebook.xml
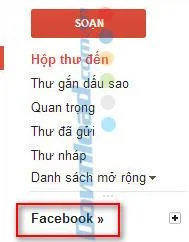
Step 8: Return to the main page of Gmail , you will see the bottom of the Facebook page . You click on this utility to log into Facebook as usual.
So you have one more way to access the world's largest social network, that is, to Facebook with Gmail.
I wish you successful implementation!
Follow SUSE’s SP7 procedure to enable FIPS mode, reboot safely, verify the active policy, and check whether your compliance requirement calls for validated modules.
Compare YaST and cryptsetup for a new encrypted SLES data volume, choose LUKS1 or LUKS2, and verify unlock and mount behavior safely.
Create, refine, and verify a least-privilege AppArmor profile on SLES 15 SP7, with a clear note on SLES 16’s SELinux default.
Set up RMT on SLES 15, mirror entitled repositories, and verify HTTPS registration and package access from a test client.
Connect SLES 15 to AD with YaST’s SSSD-based logon management, then verify directory lookup, domain login, and Kerberos tickets.
Set up the right Live Patching path for SLES 16.0 or 15 SP7, apply eligible kernel fixes, and confirm what is active without confusing it with a reboot-required kernel update.
Load a custom SLES 15 kernel module without disabling Secure Boot. Match the running kernel, sign the .ko file, enroll a MOK key, and verify loading.
SLES 15 SP5 can migrate online to SP6, but each node must reboot. Use a tested rolling upgrade or blue-green cutover to keep workloads reachable.
Use SUSE’s supported STIG profile to scan SLES 15, test remediation, review remaining findings, and retain assessment evidence.
Trace a failed Cockpit connection through DNS, port 9090, the systemd socket, firewalld, TLS, and login settings using current SUSE guidance.