How to hide online status on Viber

Viber is a popular VoIP application in Vietnam, allowing users to message or call completely free. Just open 3G or Wifi, you can freely chat until your phone runs out of battery! The benefits of Viber are undeniable, but sometimes you feel annoyed with some of the utilities that Viber offers.

Viber for iOS Viber for Android

Sometimes you want to hide Viber, do not want others to see you are online to avoid nuisance? Or do not want others to know you have seen "Seen" content in the conversation? This article, Download.com.vn will give you tips to hide online status, hide content in Viber conversation for phones.

Viber now has updated a lot of new special features, you can also play games directly on Viber. You can update or download the latest version to experience the advantages of the leading free chat application today.

Instructions for hiding online status on Viber

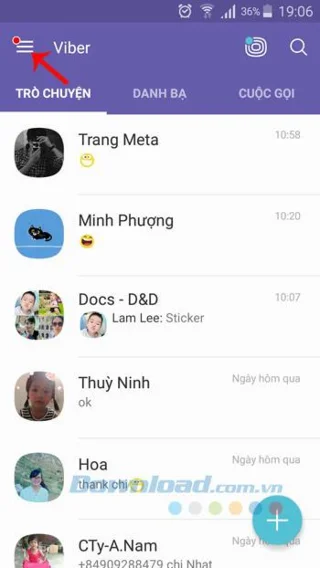
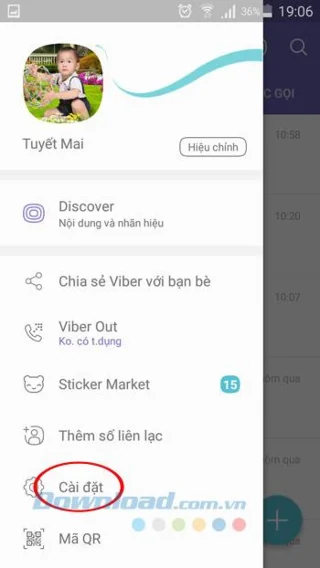
Step 1: Open the Viber app on your phone, click the 3 dash icon in the top left corner of the screen, select Settings.
How to hide online status on ViberHow to hide online status on Viber

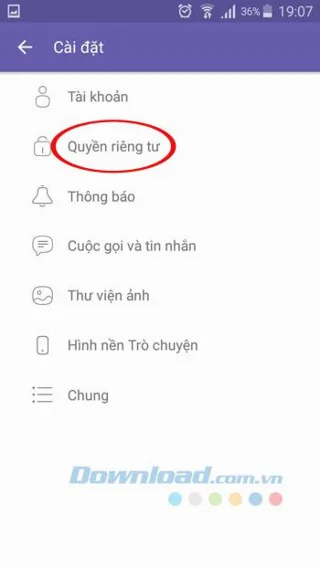
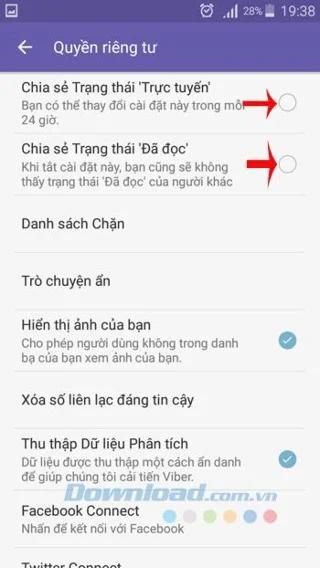
Step 2: Next, click on Privacy, uncheck the 2 items:

  • Share 'online' status: All friends will not see when you are online. But you need to note, after unchecking, it takes 24 hours to reset.
  • Share 'Read' Status : Hide the read status (Seen) for messages, so friends don't know whether you've read the message or not.

How to hide online status on ViberHow to hide online status on Viber

Video tutorial offline online status on Viber

From now on every other person you know will not know, to avoid being bothered while busy. You can do the same on iOS and Windows Phone devices.

I wish you successful implementation!
Leave a Comment

Enable FIPS Mode on SLES 15 and Verify the Boot State

Enable FIPS Mode on SLES 15 and Verify the Boot State

Follow SUSE’s SP7 procedure to enable FIPS mode, reboot safely, verify the active policy, and check whether your compliance requirement calls for validated modules.

Set Up a LUKS-Encrypted Data Volume on SLES

Set Up a LUKS-Encrypted Data Volume on SLES

Compare YaST and cryptsetup for a new encrypted SLES data volume, choose LUKS1 or LUKS2, and verify unlock and mount behavior safely.

Build a Custom AppArmor Profile on SUSE Linux

Build a Custom AppArmor Profile on SUSE Linux

Create, refine, and verify a least-privilege AppArmor profile on SLES 15 SP7, with a clear note on SLES 16’s SELinux default.

Build a Local SUSE Update Server with RMT on SLES 15

Build a Local SUSE Update Server with RMT on SLES 15

Set up RMT on SLES 15, mirror entitled repositories, and verify HTTPS registration and package access from a test client.

Join SLES 15 to Active Directory with SSSD in YaST

Join SLES 15 to Active Directory with SSSD in YaST

Connect SLES 15 to AD with YaST’s SSSD-based logon management, then verify directory lookup, domain login, and Kerberos tickets.

Enable SLES Live Patching and Verify a Kernel Fix

Enable SLES Live Patching and Verify a Kernel Fix

Set up the right Live Patching path for SLES 16.0 or 15 SP7, apply eligible kernel fixes, and confirm what is active without confusing it with a reboot-required kernel update.

Install and Sign Custom Kernel Modules on SLES 15 Secure Boot

Install and Sign Custom Kernel Modules on SLES 15 Secure Boot

Load a custom SLES 15 kernel module without disabling Secure Boot. Match the running kernel, sign the .ko file, enroll a MOK key, and verify loading.

Keep Services Available During a SLES 15 SP5 to SP6 Upgrade

Keep Services Available During a SLES 15 SP5 to SP6 Upgrade

SLES 15 SP5 can migrate online to SP6, but each node must reboot. Use a tested rolling upgrade or blue-green cutover to keep workloads reachable.

Apply the SLES 15 STIG Safely with OpenSCAP

Apply the SLES 15 STIG Safely with OpenSCAP

Use SUSE’s supported STIG profile to scan SLES 15, test remediation, review remaining findings, and retain assessment evidence.

Restore Cockpit Access to SUSE Linux Enterprise Server

Restore Cockpit Access to SUSE Linux Enterprise Server

Trace a failed Cockpit connection through DNS, port 9090, the systemd socket, firewalld, TLS, and login settings using current SUSE guidance.