Kawaii Halloween Decor Without Gore or Jump Scares
Create a gentle Halloween look with pastel colors, friendly ghosts, easy no-carve accents, and practical safety tips for your home.
The article tested 3 different passwords with an open source password cracking tool to find out which method really works when it comes to password security.
Table of Contents
When you create an account with an online service, the provider typically encrypts your login information on their servers. This is done using an algorithm to create a “hash,” a seemingly unique random string of letters and numbers for your password. Of course, it’s not actually random, but a very specific string of characters that only your password could generate, but to the untrained eye, it looks like a jumbled mess.
It's much faster and easier to turn a word into a hash than to "decode" the hash back into a word. So when you set up a password, the service you're logging into will run your password through the hash and store the result on their servers.
If this password file is leaked, hackers will try to find out its contents by cracking the passwords. Since encrypting passwords is faster than decrypting them, hackers will set up a system that takes potential passwords as input, encrypts them using the same method as the server, and then compares the results to the password database.
If the hash of a potential password matches any entry in the database, the hacker knows that every attempt matches the potential password tried.
Let’s try cracking some of the passwords this article has generated to see how easy it is. To do this, we’ll use Hashcat , a free and open source password cracking tool that anyone can use.
For these tests, the example will crack the following passwords:
Now, let's encrypt the passwords using MD5. Here's how the passwords would look if they were in a saved password file:
Now, it's time to crack them.
To start, let's perform a Dictionary Attack, one of the most common password attack methods. This is a simple attack where a hacker takes a list of potential passwords, asks Hashcat to convert them to MD5, and sees if any of them match the three entries above. For this test, let's use the file "rockyou.txt" as our dictionary, which was one of the largest password leaks in history.
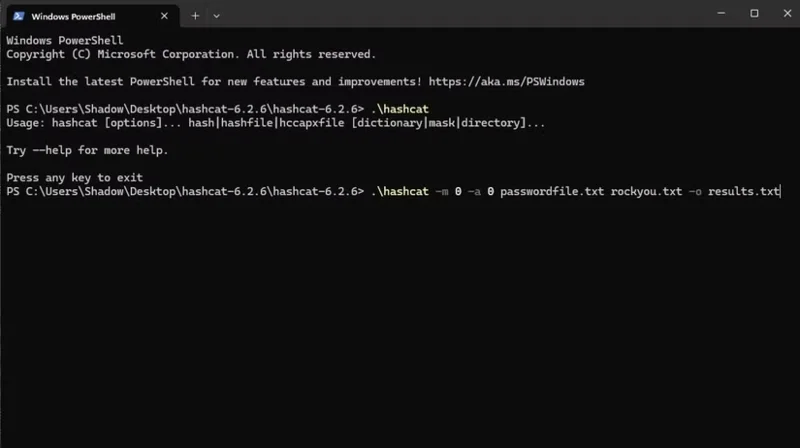
To start cracking, the author of the article went to the Hashcat folder, right-clicked on an empty space and clicked Open in Terminal . Now that the Terminal was open and set to the Hashcat folder, invoked the Hashcat application with the following command:
.\hashcat -m 0 -a 0 passwordfile.txt rockyou.txt -o results.txtHere is what the command does:
Despite the large size of rockyou, Hashcat processed all of them in 6 seconds. In the resulting file, Hashcat says it cracked the password 123456, but the passwords Susan and Bitwarden were not cracked. This is because 123456 was used by someone else in the rockyou.txt file, but no one else used the passwords Susan or Bitwarden, meaning they were secure enough to survive this attack.
Dictionary Attacks are effective when someone uses the same password as one found in a large password list. They are quick and easy to perform, but they cannot crack passwords that are not in the dictionary. Therefore, if you really want to test your password, you need to use Brute Force attacks.
While Dictionary Attacks are just taking a pre-set list and switching them one by one, Brute Force attacks do the same but with every conceivable combination. They are harder to execute and take longer, but they will eventually crack any password. As we will soon see, that can sometimes take a very long time.
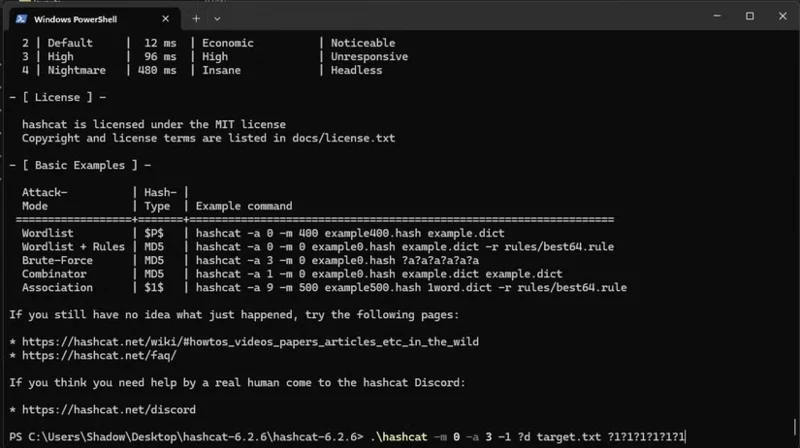
Here is the command used to perform a "real" Brute Force attack:
.\hashcat -m 0 -a 3 target.txt --increment ?a?a?a?a?a?a?a?a?a?a -o output.txtHere is what the command does:
Even with this terrible mask, the password 123456 is cracked in 15 seconds. Despite being the most common password, it is one of the weakest.
The password "Susan48!" is much better - the computer says it will take 4 days to crack. However, there is a problem. Remember when the article said that Susan's password had some serious flaws? The biggest flaw is that the password is constructed in a predictable way.
When we create passwords, we often put specific elements in specific places. Imagine the password creator Susan tried using “susan” at first but was asked to add a capital letter and a number. To make it easier to remember, they capitalized the first letter and added the numbers at the end. Then, perhaps a login service asked for a symbol, so the password creator tacked it on at the end.
So, we can use a mask to tell Hashcat to only try specific characters in specific places to exploit how easy it is for people to guess passwords. In this mask, "?u" will only use uppercase letters in that place, "?l" will only use lowercase letters, and "?a" represents any character:
.\hashcat -m 0 -a 3 -1 ?a target.txt ?u?l?l?l?l?a?a?a -o output.txtWith this mask, Hashcat cracked the password in 3 minutes and 10 seconds, much faster than 4 days.
The Bitwarden password is 10 characters long and doesn't use any predictable patterns, so it took a Brute Force attack without any masks to crack it. Unfortunately, when asking Hashcat to do so, it gave an error saying that the number of possible combinations exceeded the integer limit. The IT security expert said that the Bitwarden password would take 3 years to crack, so that was good enough.
The main factors that prevent the article from cracking a Bitwarden password are its length (10 characters) and unpredictability. Therefore, when creating a password, try to make it as long as possible and distribute symbols, numbers, and uppercase letters evenly throughout the password. This prevents hackers from using masks to predict the location of each element and makes it much harder for them to crack.
You're probably familiar with the old password adages like "use a character array" and "make it as long as possible." Hopefully, you know why people recommend these helpful tips—they're the key difference between an easy-to-crack password and a secure one.
Create a gentle Halloween look with pastel colors, friendly ghosts, easy no-carve accents, and practical safety tips for your home.
Create a spooky office cubicle with Halloween desk decor ideas that keep your workspace usable, tidy, and mindful of workplace safety.
Plan a recognizable Halloween 2026 look with pop culture costumes inspired by Spider-Man, Supergirl, Toy Story 5, Moana, Mario, and Wednesday.
Sort leftover Halloween candy safely, share or repurpose sealed treats, and choose food use or compost for pumpkins based on their condition.
Compare workplace Halloween costume choices by respect, dress code, mobility, and safety—and learn when a subtle accessory or a policy check is the better option.
Find a couples costume that fits your style, budget, and comfort level, from Addams Family classics to original inside-joke duos.
Need a last-minute high school Halloween costume? Compare 10 easy closet-based ideas by prep time, comfort, school-day practicality, and simple safety checks.
Use a simple 2026 Halloween decorating timeline for indoor décor, outdoor displays, and fresh pumpkins, with practical adjustments for weather and events.
Mix five vivid, approachable Halloween cocktails with measured recipes, simple prep tips, and an alcohol-free option for your party guests.
Find 15 office-friendly Halloween costume ideas for 2026, with practical checks for dress codes, respectful themes, comfort, and workplace safety.