Keep Writer Revisions Visible When Exporting to DOCX

Track edits in Writer, preserve an editable ODT source, and check the exported DOCX in Word before sharing it.
The feature to block spam software has officially appeared on the Microsoft Edge web browser . With this Crapware blocker we will minimize the installation of automatic junk software and help the system operate stably and permanently.
Currently Crapware Blocker is not the default feature, you need to enable it to work when launching Microsoft Edge browser. Accordingly Crapware Blocker feature can block most obnoxious applications such as adware , trackers, browser toolbars, etc. Please follow the instructions below to activate Crapware Blocker on Microsoft Edge now.
Step 1:
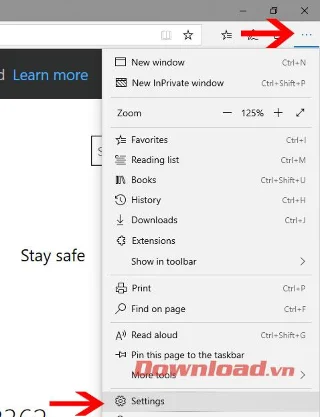
At the main interface, click the three dot menu (top right corner) → Settings .
Step 2:
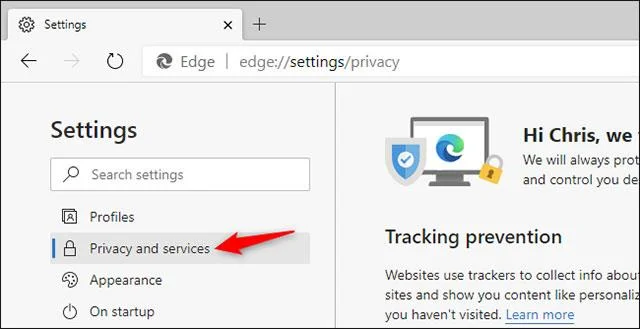
The Settings window appears, select Privacy and services.
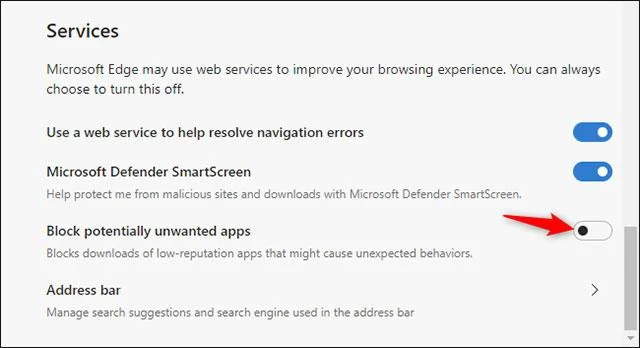
Here, find the Block potentially unwanted apps section and turn it on.
If you don't see this feature, quickly update Microsoft Edge to the latest version by going to Settings → Help & feedback → About Microsoft Edge.
Above we have shown you how to enable the latest junk software on Microsoft Edge. Hope this feature will be really useful for the system being used.
Track edits in Writer, preserve an editable ODT source, and check the exported DOCX in Word before sharing it.
Follow SUSE’s SP7 procedure to enable FIPS mode, reboot safely, verify the active policy, and check whether your compliance requirement calls for validated modules.
Compare YaST and cryptsetup for a new encrypted SLES data volume, choose LUKS1 or LUKS2, and verify unlock and mount behavior safely.
Create, refine, and verify a least-privilege AppArmor profile on SLES 15 SP7, with a clear note on SLES 16’s SELinux default.
Set up RMT on SLES 15, mirror entitled repositories, and verify HTTPS registration and package access from a test client.
Connect SLES 15 to AD with YaST’s SSSD-based logon management, then verify directory lookup, domain login, and Kerberos tickets.
Set up the right Live Patching path for SLES 16.0 or 15 SP7, apply eligible kernel fixes, and confirm what is active without confusing it with a reboot-required kernel update.
Load a custom SLES 15 kernel module without disabling Secure Boot. Match the running kernel, sign the .ko file, enroll a MOK key, and verify loading.
SLES 15 SP5 can migrate online to SP6, but each node must reboot. Use a tested rolling upgrade or blue-green cutover to keep workloads reachable.
Use SUSE’s supported STIG profile to scan SLES 15, test remediation, review remaining findings, and retain assessment evidence.








