Epic Games Launcher is a tool for downloading and playing games distributed on the Epic Games Store - a new game store similar to the Uplay or Steam we have known.
This Epic Games Launcher game management software proved extremely useful in supporting gamers to download and play games on PC smoothly, effectively right on the computer.
Epic Games Launcher
No limit on the number and genre of games like Gamota Launcher or Garena , Epic Games Launcher brings together all the games from different brands for players to choose. Dauntless - blockbuster action monster theme game is a specific example.
Right now, if you want to experience with Epic Games Launcher, you can follow this tutorial.
How to download and install Epic Games Launcher on a PC
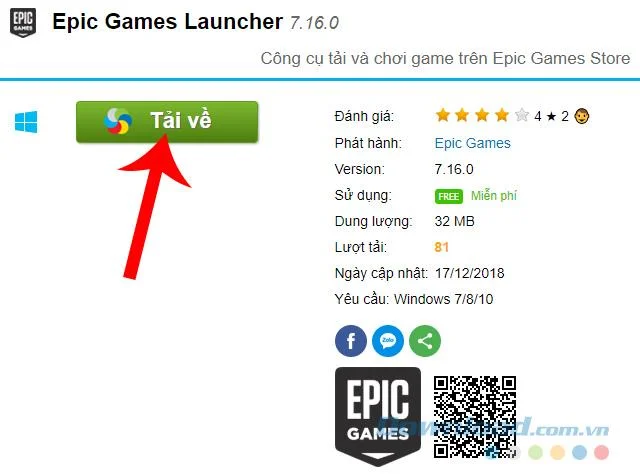
Step 1: You access the support page to download Epic Games Launcher to your computer - https://download.com.vn/epic-games-launcher/download and select Download .
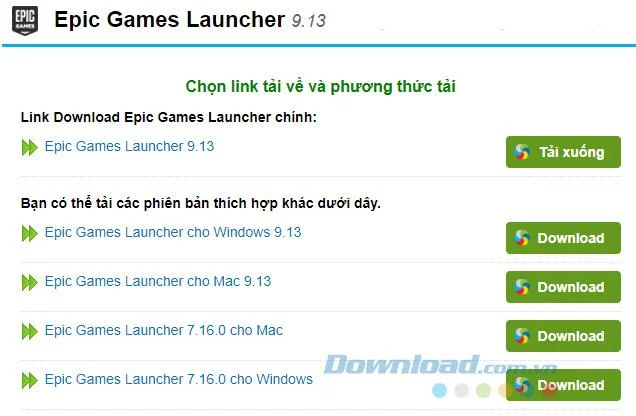
Step 2: In the next interface, left-click Download or click directly on one of the links below.

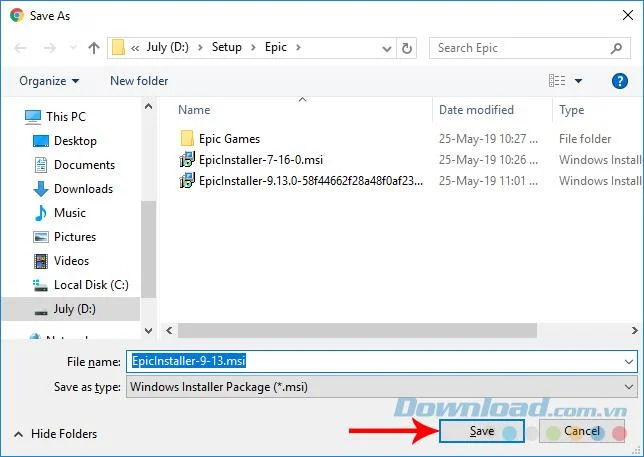
Step 3: Choose a location to save the Epic Games Launcher installation file and then Save again.

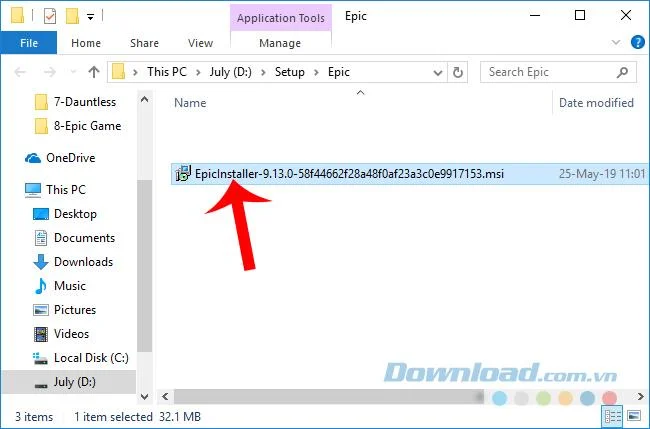
Step 4: Open the folder, double-click the file to start the installation.

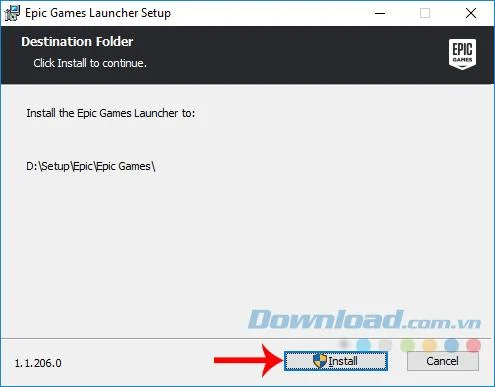
Step 5: Click Install to install Epic Games Launcher on the computer .

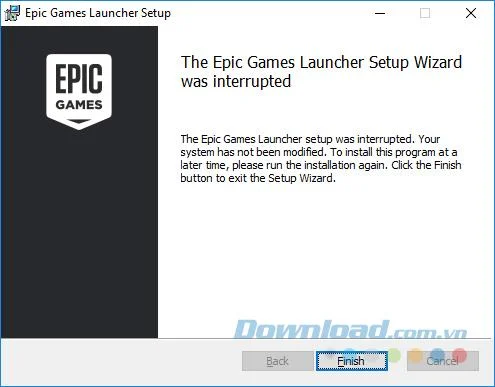
Step 6: Wait until the installation process is completed, click Finish to close this window and start Epic Games Launcher always.

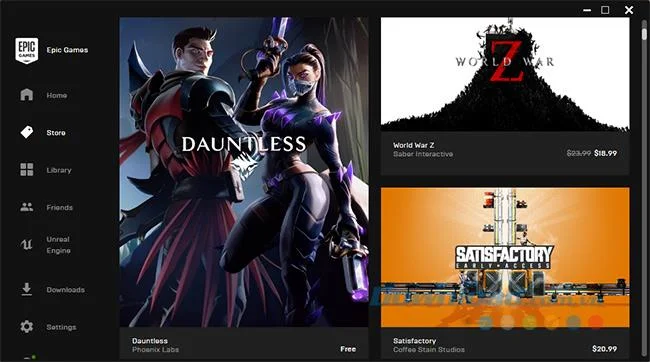
And this is the main interface of Epic Games Launcher. Here, we can search, download games, organize and manage the PC games we have easily. You can also use Epic Games' gameonline store ( Epic Games Store ) to search with similar features.
 The main interface of Epic Games Launcher
Video for installing Epic Games Launcher:
 The main interface of Epic Games Launcher









