Home
» How to
»
How to activate and use Windows Sandbox on Windows 10
How to activate and use Windows Sandbox on Windows 10
Video How to activate and use Windows Sandbox on Windows 10
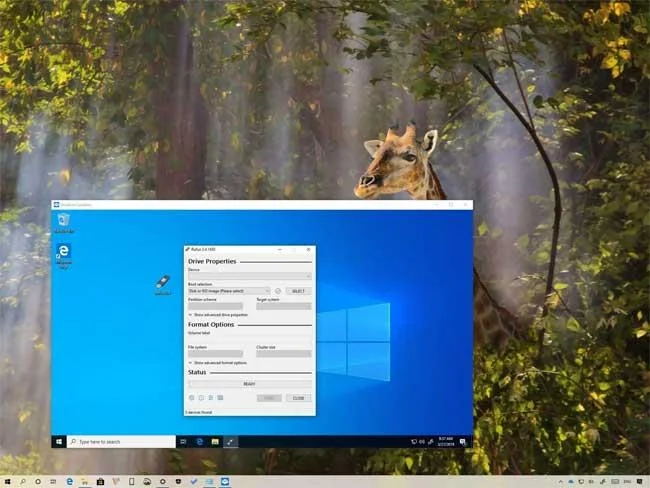
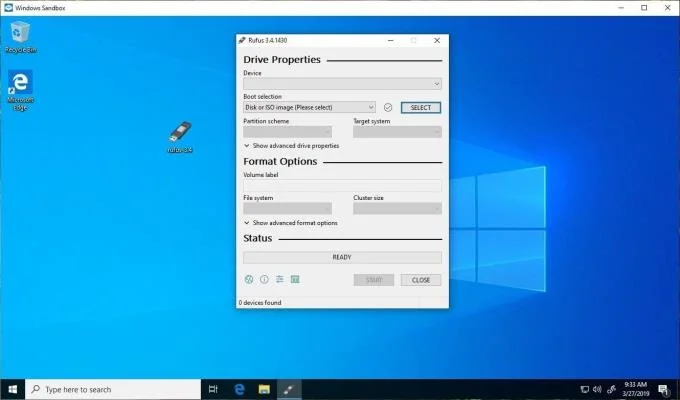
Windows Sandbox is a new feature in the Windows 10 May 2019 update (version 1903), designed to run unreliable applications in isolated virtualized environments.
If you need to run the application but are not sure about its safety, the Windows 10 May 2019 update includes a Windows Sandbox feature that supports users to perform this task without affecting the system if there is an error. happening.
Technically, Windows Sandbox is a virtual machine created on demand using Microsoft's hypervisor virtualization using the same copy of the operating system on your computer. However, it is an ultra-light environment, only about 100 MB, which has been optimized to boot and run faster. It focuses on security, working more efficiently by using integrated kernel calendar, virtualization graphics and intelligent memory management.
Although, you can create virtual machines to have the same experience thanks to third-party software such as VirtualBox , VMware Workstation ... but Windows Sandbox offers some outstanding benefits. For example, you do not need to take additional steps to create or load a virtual machine. Every time you open the feature, it runs a clean and new installation of Windows 10. When the application is finished and the Windows Sandbox is closed, all data will be automatically deleted. In addition, using virtualization isolates everything that happens inside this environment with an installation of the main operating system which increases the maximum level of security when testing unreliable applications. Here's how to use Windows Sandbox in Windows 10 May 2019 Update.
Before turning on and using Windows Sandbox, your device must meet the following minimum hardware & software requirements:
Windows 10 Pro (or Enterprise).
Hardware virtualization.
AMD64 architecture.
Minimum 2-core processor (4-core recommended with hyperthreading technology).
4 GB RAM (8 GB recommended).
1 GB free hard disk space (SSD recommended).
How to activate Windows Sandbox on Windows 10
The process is really simple thanks to the preeminent features of Windows 10.
Turn on virtualization
Before you can activate Windows Sandbox, you must ensure that the device you are using supports virtualization hardware and this feature is enabled in Basic Input / Output System (BIOS) or Unified Extensible Firmware Interface (UEFI).
Check if the device supports virtualization as follows:
1. Open Start .
2. Find Command Prompt and click on the first result.
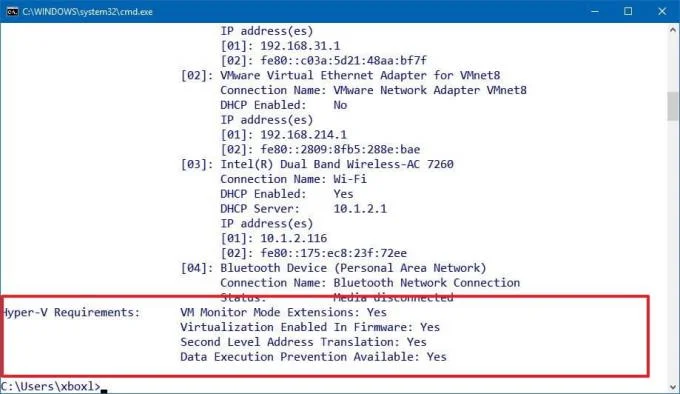
3. Type command: systeminfo.exe and press Enter .
4. In the " Hyper-V Requirements " section. If " Virtualization Enabled In Firmware " shows Yes . You can then use Windows Sandbox.
If virtualization is not enabled, you need to open the device in BIOS BIOS or UEFI and enable this feature. This process usually requires pressing one of the function keys (F1, F2, F3, F10, F12), ESC or Delete as soon as the computer boots up. However, the installation will vary by manufacturer, even PC model. Therefore, check your device manufacturer's support web site for more specific instructions.
Activate Windows Sandbox
To turn on Windows Sandbox on Windows 10 version 1903, follow these steps:
1. Open Start .
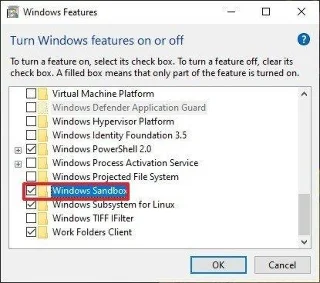
2. Find Turn Windows features on or off and click on the first result to open the experience of Windows features.
3. Check the Windows Sandbox option .
4.Click the OK button .
5.Click the Restart now button .
After completing the steps above, you can start using the new virtualization environment to temporarily install and test untrusted applications.
How to use Windows Sandbox on Windows 10
Windows Sandbox is very easy to use, just follow these steps:
1. Open Start.
2. Search for Windows Sandbox, right-click on the first result and select Run as administrator .
3. On the physical device, right-click the application installer that you want to test, select Copy .
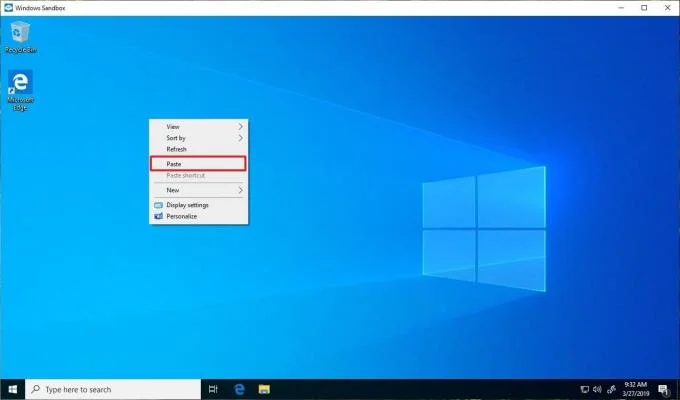
4. Inside the Windows Sandbox environment, right-click the desktop and select Paste to transfer the executable file (.exe).
Quick tip : Although you can't drag and drop apps from the main installation in Windows Sandbox to transfer files, you can download app files using Microsoft Edge .
5. Double-click the installation file (.exe, .msi, etc) to launch it.
6. Continue to follow the instructions on the screen to complete the installation process.
After completing all the steps above, you can start using the normal untrusted application like any other software. Alternatively, you can use Ctrl + Alt + Break (or Pause) to enter and exit Windows Sandbox in full screen mode. If you want to use high contrast mode, inside the virtualization experience, you can use the key combination Shift + Alt + PrintScreen to activate it.
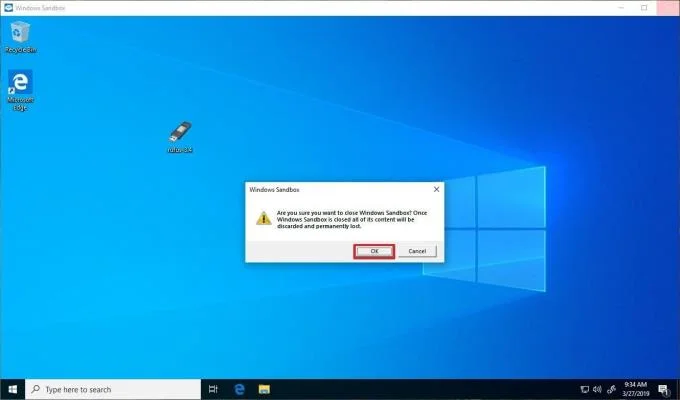
After finishing testing the application, click the X button in the upper right corner, then, click OK to close the Sandbox. At the end of the experience, the virtual machine and its content will be permanently deleted from your device without affecting the Windows 10 system.
Run Windows Sandbox inside the virtual machine
If you are trying to use Windows Sandbox in a virtual machine, you need to set up a system that allows running nested virtualization, that is, running the virtualization environment in the virtual machine.
In the virtual machine, type powershell in the Start Menu search bar , right-click on Best Match and select Run as Administrator .
Swap <VMName> to the virtual machine name. Restart the virtual machine. You will then see the Windows Sandbox option located on the Start Menu.
Run Windows Sandbox on Windows 10 Home
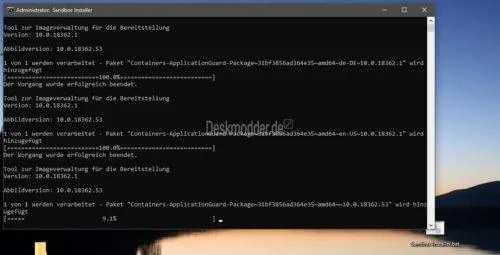
In fact, Windows Sandbox cannot run on Windows 10 Home. However, thanks to a patch developed by the Deskmodder team , Windows 10 Home users were able to launch Windows Sandbox.
If you want to try running Windows Sandbox on Windows 10 Home , make a system backup before running this patch.
Above is how to use Windows Sandbox in Windows 10 May 2019 Update . Hope the article is helpful to you.