Home
» How to
»
How to take screenshots for Samsung TVs
How to take screenshots for Samsung TVs
Television screen capture is one of the effective applications to help viewers save impressive and memorable images that appear on TV. The following article will guide you on how to take screenshots on Samsung TVs .
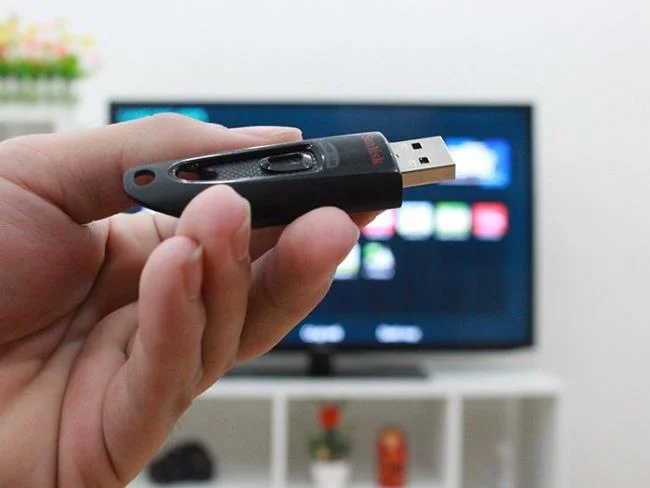
Step 1: Before taking screenshots on Samsung TV, please pair the USB storage device or HDD.
Pair the USB to the TV
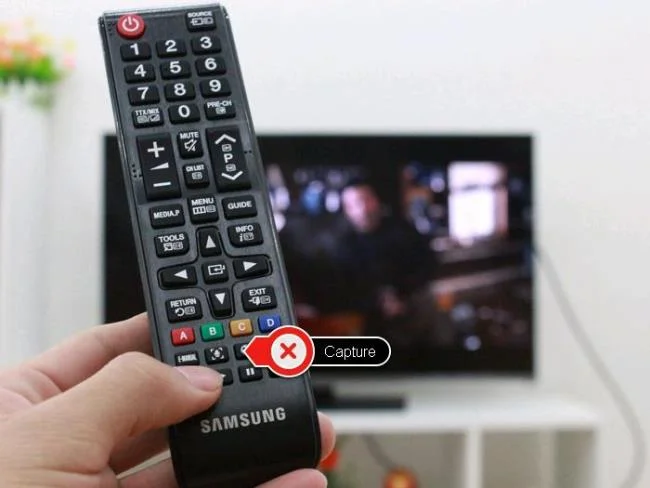
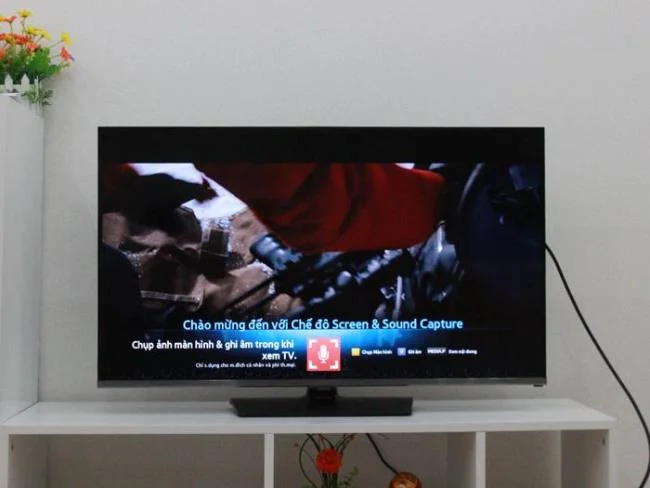
Step 2 : Click the Capture button on the TV remote. Then, on the TV screen, a message on how to take the screen will appear.
Click the capture buttonInstruction message line
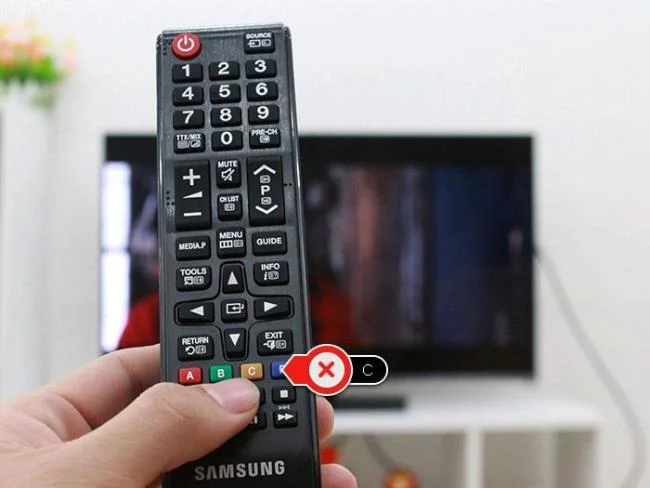
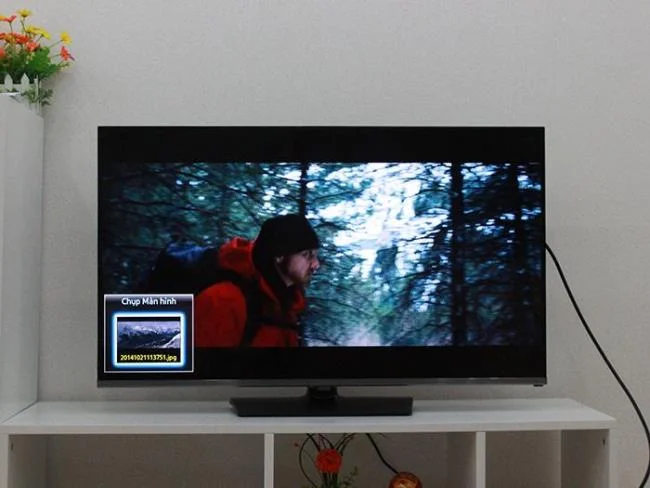
Step 3: Select the C button on the remote to take a screenshot. The captured image will be displayed as a small box in the lower left corner of the screen.
Press the C key on the remote to take a screenshotThe successful shot is displayed in the corner of the screen
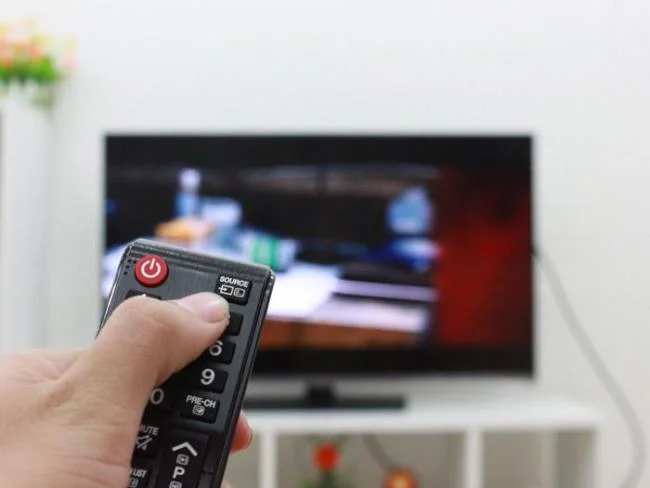
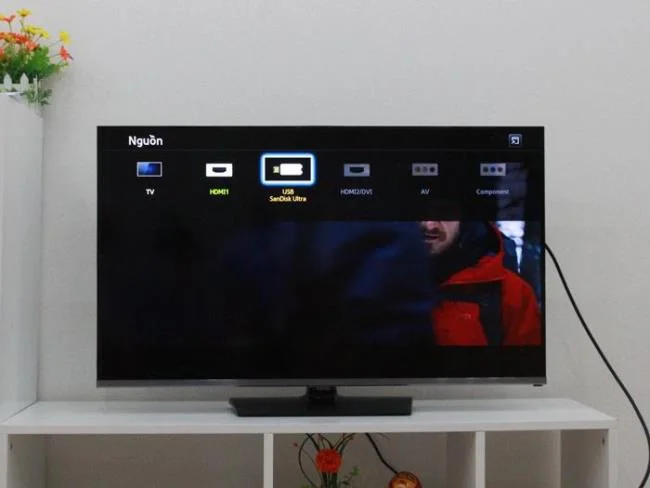
Step 4: When you want to review the captured image, select the Source button on the Remote and select the storage device.
Select the SOURCE button on the remote to view the pictureSelect a storage device
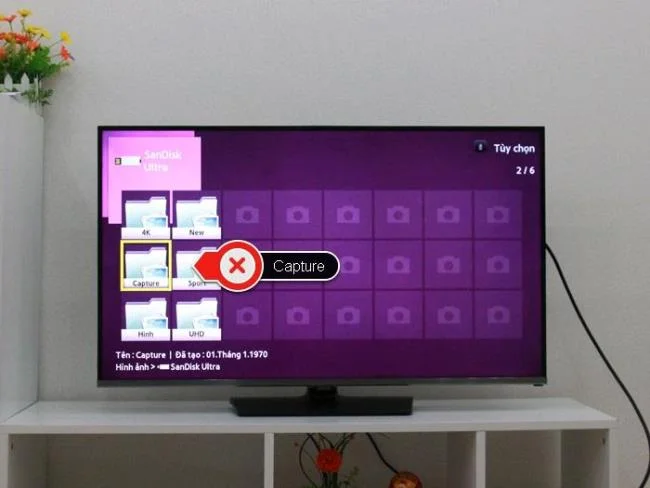
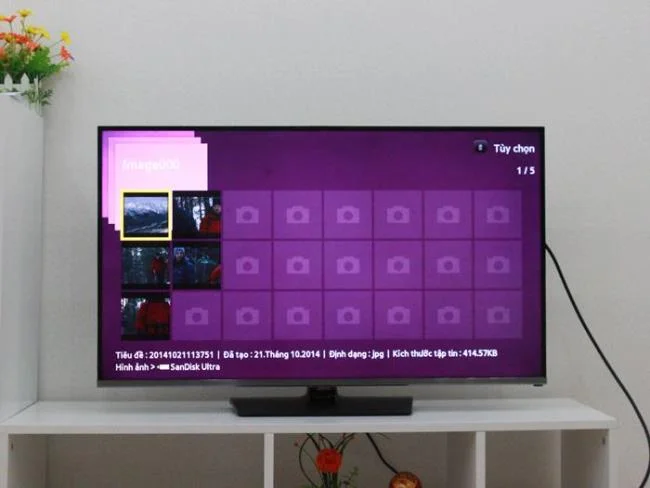
Step 5: At this point, inside the storage device will appear a new folder called Capture, you choose to see the pictures just taken. After that, you can view normal photos such as watching pictures stored on USB ( How to watch movies, watch photos, listen to music on TV via USB port )
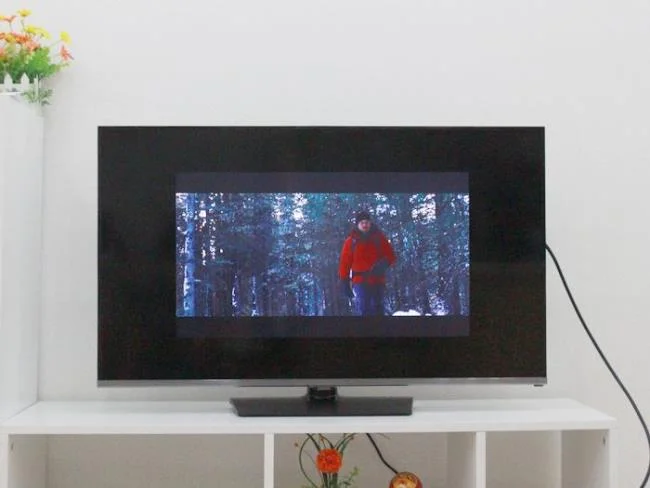
Select a folder called Capture to view the imagesSelect pictures to seeThe captured image is displayed on the television screen
So you've completed the screen capture operation with your Samsung TV , it's easy to have a collection of your own images and it's also easy to capture the memorable moments of a TV series. Favorite picture or an idol character, right? Experience this application and share with WebTech360 right below!