Enable FIPS Mode on SLES 15 and Verify the Boot State
Follow SUSE’s SP7 procedure to enable FIPS mode, reboot safely, verify the active policy, and check whether your compliance requirement calls for validated modules.
Instagram is a social networking application that many people use today. Like Facebook, this application also allows users to easily broadcast live videos. Especially to help us not miss the livestream videos of our favorite artists or relatives or friends, Instagram has launched the Live Video Notification feature.
After turning on live video notifications in the account where you want to follow all livestream videos, every time this person posts a live video, a notification will be sent to you. Today, Download.vn will introduce the article Instructions for turning on livestream notifications on Instagram , please refer to it.
Instructions for turning on live video notifications on Instagram
Step 1: First, we will open the Instagram application on our phone.
Step 2: Visit the personal page of the account you want to receive livestream notifications when they broadcast live videos.
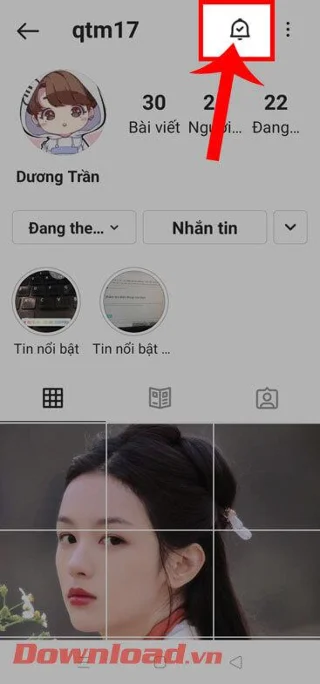
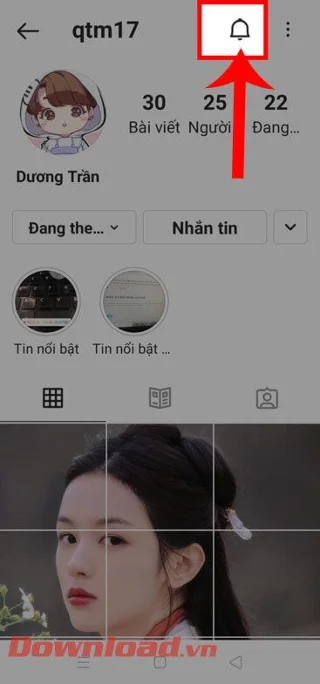
Step 3: On the personal page of the person you receive the notification from, click on the bell icon at the top of the screen.
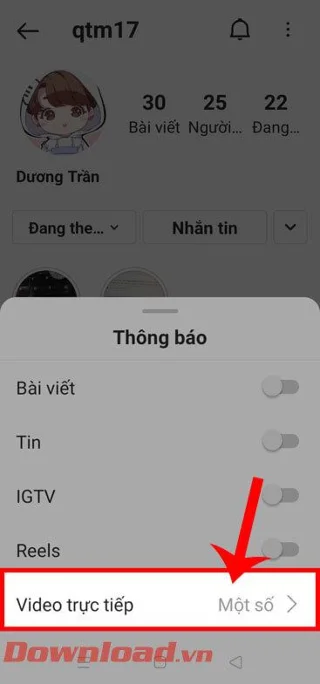
Step 4: In the Notification window at the bottom of the screen, tap Live Video.
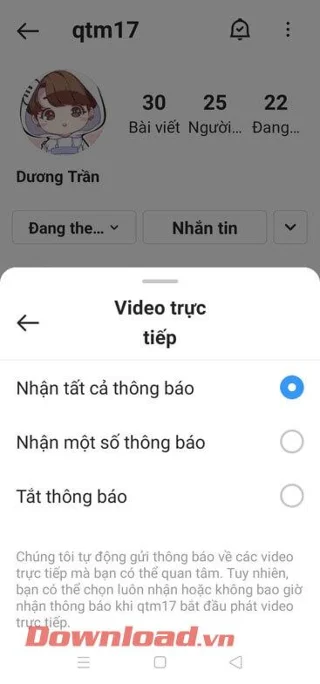
Step 5: Next, in the Live Video window , select Get all notifications.
Step 6: After setting up the Receive all live video notifications mode , the bell icon at the top of the screen will display a tick mark .
At this time, every time an Instagram user you are following posts a livestream video, you will receive a notification.
In addition, you can also refer to some other articles about Instagram tips:
Wishing you success!
Follow SUSE’s SP7 procedure to enable FIPS mode, reboot safely, verify the active policy, and check whether your compliance requirement calls for validated modules.
Compare YaST and cryptsetup for a new encrypted SLES data volume, choose LUKS1 or LUKS2, and verify unlock and mount behavior safely.
Create, refine, and verify a least-privilege AppArmor profile on SLES 15 SP7, with a clear note on SLES 16’s SELinux default.
Set up RMT on SLES 15, mirror entitled repositories, and verify HTTPS registration and package access from a test client.
Connect SLES 15 to AD with YaST’s SSSD-based logon management, then verify directory lookup, domain login, and Kerberos tickets.
Set up the right Live Patching path for SLES 16.0 or 15 SP7, apply eligible kernel fixes, and confirm what is active without confusing it with a reboot-required kernel update.
Load a custom SLES 15 kernel module without disabling Secure Boot. Match the running kernel, sign the .ko file, enroll a MOK key, and verify loading.
SLES 15 SP5 can migrate online to SP6, but each node must reboot. Use a tested rolling upgrade or blue-green cutover to keep workloads reachable.
Use SUSE’s supported STIG profile to scan SLES 15, test remediation, review remaining findings, and retain assessment evidence.
Trace a failed Cockpit connection through DNS, port 9090, the systemd socket, firewalld, TLS, and login settings using current SUSE guidance.