Enable FIPS Mode on SLES 15 and Verify the Boot State
Follow SUSE’s SP7 procedure to enable FIPS mode, reboot safely, verify the active policy, and check whether your compliance requirement calls for validated modules.
Skype is one of the applications developed by Microsoft to make it easy for people to text and call online.
When we're at work and constantly disturbed by Skype messages, this can also affect our work. Therefore, it is necessary to hide Skype nick while online. If you do not know how to do this, the following article will teach people how to hide Skype nick while online , invite you to follow.
Download Skype on Windows Download Skype on Mac
Step 1: Log in to your Skype account on the computer.
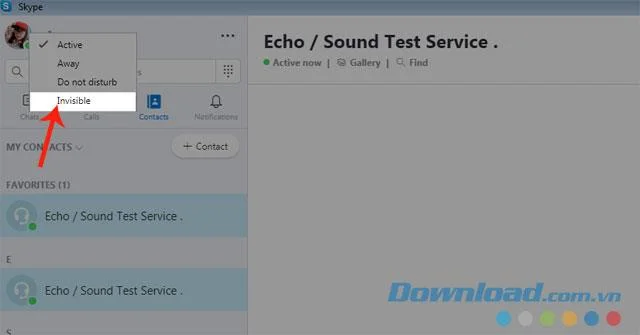
Step 2: Click on your avatar in the corner of the screen.
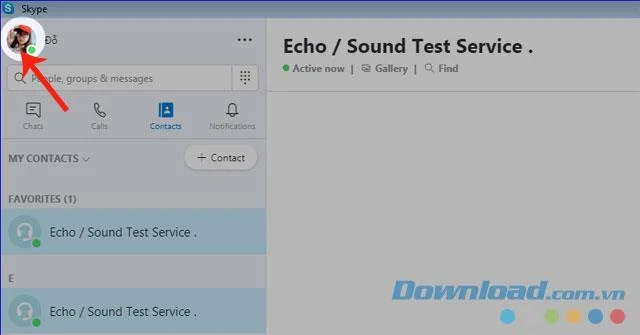
Step 3: Select Invisible .
Download Skype on Android Download Skype on IOS
Step 1: Access your Skype account on your phone.
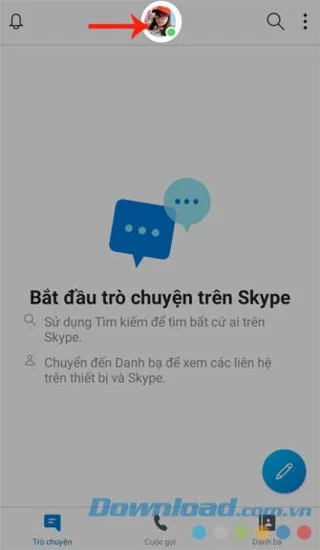
Step 2: Click your avatar at the top of the screen.
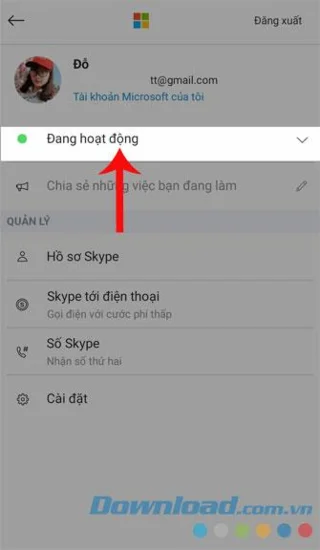
Step 3: Click the Active item .
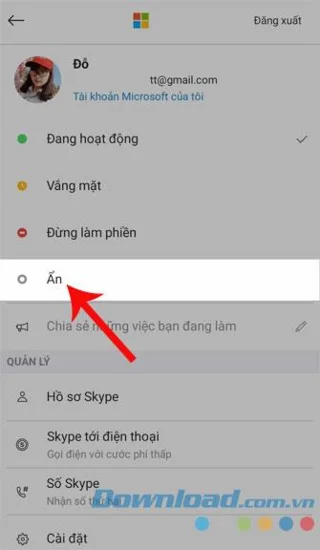
Step 4: Select Hide .


Above is a guide to hide Skype nick while online, we hope that after referencing and implementing the above methods, people will not be afraid of being disturbed from messages while working anymore. In addition, you can refer to some other articles such as: How to hide Skype IP address , How to change personal information of Skype account , ....
I wish you successful implementation!
Follow SUSE’s SP7 procedure to enable FIPS mode, reboot safely, verify the active policy, and check whether your compliance requirement calls for validated modules.
Compare YaST and cryptsetup for a new encrypted SLES data volume, choose LUKS1 or LUKS2, and verify unlock and mount behavior safely.
Create, refine, and verify a least-privilege AppArmor profile on SLES 15 SP7, with a clear note on SLES 16’s SELinux default.
Set up RMT on SLES 15, mirror entitled repositories, and verify HTTPS registration and package access from a test client.
Connect SLES 15 to AD with YaST’s SSSD-based logon management, then verify directory lookup, domain login, and Kerberos tickets.
Set up the right Live Patching path for SLES 16.0 or 15 SP7, apply eligible kernel fixes, and confirm what is active without confusing it with a reboot-required kernel update.
Load a custom SLES 15 kernel module without disabling Secure Boot. Match the running kernel, sign the .ko file, enroll a MOK key, and verify loading.
SLES 15 SP5 can migrate online to SP6, but each node must reboot. Use a tested rolling upgrade or blue-green cutover to keep workloads reachable.
Use SUSE’s supported STIG profile to scan SLES 15, test remediation, review remaining findings, and retain assessment evidence.
Trace a failed Cockpit connection through DNS, port 9090, the systemd socket, firewalld, TLS, and login settings using current SUSE guidance.